第352篇:一次完整的网络健康检查(Health Check)
关键词:Health Check、网络巡检、配置核查、性能评估、风险识别
一、案例背景
某互联网企业委托专业网络服务团队对其全网进行一次深度健康检查(Health Check)。该网络包含3个数据中心、15个办公地点、约200台网络设备。企业IT团队日常运维繁忙,缺乏系统性的健康检查机制,希望通过本次检查发现潜在风险。
检查范围: - 数据中心网络:3个(北京、上海、深圳) - 办公网络:15个 - 网络设备总数:约200台 - 网络类型:核心交换、接入交换、路由、防火墙、无线
二、需求分析与方案设计
2.1 健康检查维度
| 维度 | 检查内容 | 权重 |
|---|---|---|
| 设备健康 | CPU/内存/温度/电源/风扇 | 20% |
| 配置规范 | 配置合规性/最佳实践 | 25% |
| 链路质量 | 链路利用率/误码率/丢包 | 15% |
| 协议状态 | OSPF/BGP/MPLS/STP状态 | 15% |
| 安全合规 | 访问控制/认证/加密 | 15% |
| 文档完整 | 拓扑/配置/IP地址文档 | 10% |
2.2 检查流程
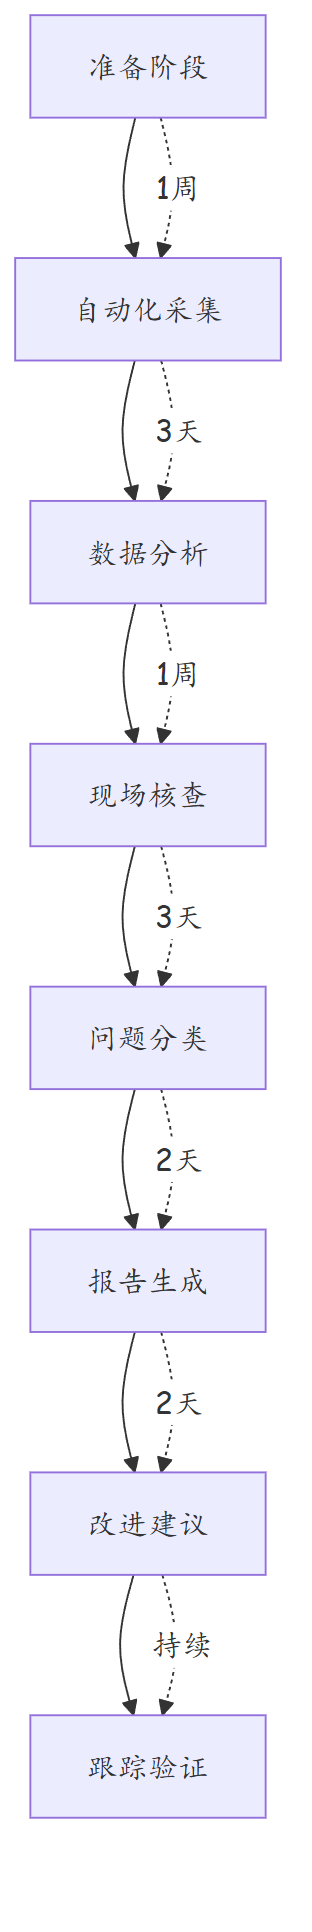
2.3 评分体系
| 等级 | 分数 | 说明 |
|---|---|---|
| 优秀 | 90-100 | 网络状态良好,少量优化建议 |
| 良好 | 75-89 | 网络状态正常,存在改进空间 |
| 一般 | 60-74 | 存在中等风险,需要关注 |
| 较差 | 40-59 | 存在高风险,需要立即整改 |
| 危险 | 0-39 | 存在严重风险,可能影响业务 |
三、技术细节与实施过程
3.1 自动化采集脚本
# health_check_collect.py - 健康检查数据采集脚本
import paramiko
import json
from datetime import datetime

devices = load_device_list("devices.json")
results = {}

for device in devices:
    ssh = paramiko.SSHClient()
    ssh.set_missing_host_key_policy(paramiko.AutoAddPolicy())
    ssh.connect(device["ip"], username=device["user"], password=device["password"])

    device_result = {
        "name": device["name"],
        "ip": device["ip"],
        "timestamp": datetime.now().isoformat(),
        "reachability": True,
        "hardware": {},
        "configuration": {},
        "protocols": {},
        "interfaces": {}
    }

    # 采集硬件状态
    stdin, stdout, stderr = ssh.exec_command("display device")
    device_result["hardware"] = parse_device_output(stdout.read().decode())

    # 采集CPU/内存
    stdin, stdout, stderr = ssh.exec_command("display cpu-usage")
    device_result["hardware"]["cpu"] = parse_cpu_output(stdout.read().decode())

    stdin, stdout, stderr = ssh.exec_command("display memory-usage")
    device_result["hardware"]["memory"] = parse_memory_output(stdout.read().decode())

    # 采集接口状态
    stdin, stdout, stderr = ssh.exec_command("display interface brief")
    device_result["interfaces"] = parse_interface_output(stdout.read().decode())

    # 采集协议状态
    stdin, stdout, stderr = ssh.exec_command("display ospf peer brief")
    device_result["protocols"]["ospf"] = parse_ospf_output(stdout.read().decode())

    stdin, stdout, stderr = ssh.exec_command("display bgp peer")
    device_result["protocols"]["bgp"] = parse_bgp_output(stdout.read().decode())

    # 采集配置(摘要)
    stdin, stdout, stderr = ssh.exec_command("display current-configuration | include ^[a-z]")
    device_result["configuration"]["summary"] = stdout.read().decode()

    results[device["name"]] = device_result
    ssh.close()

# 保存采集结果
with open(f"health_check_{datetime.now().strftime('%Y%m%d')}.json", "w") as f:
    json.dump(results, f, indent=2)

print(f"Collection complete: {len(results)} devices")
3.2 健康检查发现的主要问题
问题1:设备硬件隐患
| 设备 | 问题 | 风险等级 | 建议 |
|---|---|---|---|
| CE6865-Spine-02 | 风扇模块2故障 | 高 | 立即更换风扇 |
| NE40E-Core-01 | 电源1负载90% | 中 | 检查负载分布 |
| S5735-Access-15 | 温度告警(55°C) | 高 | 改善散热环境 |
问题2:配置不规范
# 发现1:弱密码
<S5735> display current-configuration | include password
# local-user admin password simple admin123  <-- 弱密码

# 发现2:SNMP v2c公开社区名
<S5735> display current-configuration | include snmp
# snmp-agent community public  <-- 默认社区名

# 发现3:未配置日志服务器
# 多台设备未配置info-center loghost
问题3:链路隐患
| 链路 | 问题 | 利用率 | 建议 |
|---|---|---|---|
| Spine01↔Leaf03 | 单链路负载>80% | 85% | 增加链路或负载优化 |
| Core↔Agg-05 | 光模块劣化 | - | 更换光模块 |
| Firewall↔Core | 无冗余链路 | - | 增加冗余链路 |
3.3 协议状态检查
# OSPF检查
<NE40E> display ospf peer brief
# 发现:NE40E与Agg-03的OSPF邻居频繁Flapping(每天3次)
# 根因:链路质量差,丢包率高

# BGP检查
<NE40E> display bgp peer
# 发现:与上游运营商的BGP会话未启用BFD
# 建议:启用BFD加速故障检测

# STP检查
<S5735> display stp brief
# 发现:部分接入交换机存在STP拓扑变更频繁(每天5次)
# 根因:终端频繁插拔导致BPDU震荡
# 建议:启用BPDU保护
四、实战配置/案例分析
4.1 问题修复配置
# 修复1:强密码策略
[Huawei] local-user admin password cipher
[Huawei] local-user admin password expire 90  # 90天过期

# 修复2:SNMP v3替代v2c
[Huawei] snmp-agent
[Huawei-snmp-agent] undo community public
[Huawei-snmp-agent] usm-user v3 admin auth-mode sha auth-cipher Huawei@123 priv-mode aes priv-cipher Huawei@456
[Huawei-snmp-agent] quit

# 修复3:日志服务器配置
[Huawei] info-center enable
[Huawei] info-center loghost 10.0.0.100
[Huawei] info-center loghost trap enable

# 修复4:BPDU保护
[Huawei] stp bpdu-protection
[Huawei] interface GigabitEthernet 0/0/1
[Huawei-GigabitEthernet0/0/1] stp edge-port enable
[Huawei-GigabitEthernet0/0/1] stp bpdu-protection
[Huawei-GigabitEthernet0/0/1] quit

# 修复5:BGP BFD
[Huawei] bgp 65001
[Huawei-bgp-65001] peer 202.97.0.1 bfd enable
[Huawei-bgp-65001] quit
4.4 健康检查完整命令清单
为确保健康检查覆盖全面,以下是按设备类型分类的标准检查命令集:
# ===== 通用检查命令(所有华为设备)=====

# 1. 硬件状态
display device                        # 设备模块状态
display temperature                   # 温度检查
display fan                           # 风扇状态
display power                         # 电源状态
display elist                         # 事件日志(硬件告警)

# 2. 资源使用
display cpu-usage                     # CPU利用率
display memory-usage                  # 内存利用率
display memory-usage memory-type all  # 详细内存分类

# 3. 接口状态
display interface brief               # 接口摘要
display interface description         # 接口描述
display interface | include Down      # 查找Down接口
display interface statistics | include error  # 错误统计

# 4. 协议状态
display ospf peer brief               # OSPF邻居
display isis peer                     # ISIS邻居
display bgp peer                      # BGP邻居
display stp brief                     # STP状态
display mpls ldp peer                 # MPLS LDP邻居

# 5. 路由检查
display ip routing-table statistics   # 路由统计
display ip routing-table | include Blackhole  # 黑洞路由

# 6. 安全配置
display current-configuration | include password  # 密码策略
display current-configuration | include snmp      # SNMP配置
display aaa local-user                  # 本地用户

# ===== 交换机专项检查 =====
display mac-address statistics          # MAC地址表统计
display vlan brief                      # VLAN摘要
display eth-trunk                       # Eth-Trunk状态
display arp statistics                  # ARP统计

# ===== 路由器专项检查 =====
display ip interface brief              # IP接口摘要
display ip dba statistics               # DBA策略统计
display nat session count               # NAT会话数

# ===== 防火墙专项检查 =====
display security-policy statistic       # 安全策略命中统计
display session count                   # 会话数
display device state                    # 设备状态(HA状态)
display firewall session table count    # 会话表使用率
4.5 自动评分脚本
# health_score_calculator.py - 自动化健康评分
import json

def calculate_health_score(check_results):
    """根据检查结果计算各项得分"""
    scores = {}

    # 设备健康评分(权重20%)
    hw_issues = 0
    for dev in check_results["devices"]:
        if dev.get("fan_status") != "OK":
            hw_issues += 2  # 风扇故障扣2分
        if dev.get("temp_status") == "Warning":
            hw_issues += 1
        if dev.get("cpu_usage", 0) > 80:
            hw_issues += 1
        if dev.get("memory_usage", 0) > 85:
            hw_issues += 1
    scores["device_health"] = max(0, 100 - hw_issues * 5)

    # 配置规范评分(权重25%)
    cfg_issues = 0
    for dev in check_results["devices"]:
        if "simple" in dev.get("password_type", ""):
            cfg_issues += 2  # 明文密码
        if "v2c" in dev.get("snmp_version", ""):
            cfg_issues += 1  # SNMP v2c
        if not dev.get("logserver_configured"):
            cfg_issues += 0.5
        if not dev.get("ntp_configured"):
            cfg_issues += 0.5
    scores["config_compliance"] = max(0, 100 - cfg_issues * 3)

    # 链路质量评分(权重15%)
    link_issues = 0
    for link in check_results["links"]:
        if link.get("utilization", 0) > 80:
            link_issues += 2
        if link.get("error_rate", 0) > 0.001:
            link_issues += 3
    scores["link_quality"] = max(0, 100 - link_issues * 4)

    # 协议状态评分(权重15%)
    proto_issues = 0
    for dev in check_results["devices"]:
        if dev.get("ospf_flapping"):
            proto_issues += 2
        if dev.get("bgp_no_bfd"):
            proto_issues += 1
        if dev.get("stp_flapping"):
            proto_issues += 1
    scores["protocol_status"] = max(0, 100 - proto_issues * 3)

    # 安全合规评分(权重15%)
    sec_issues = 0
    for dev in check_results["devices"]:
        if not dev.get("acl_on_mgmt"):
            sec_issues += 2
        if dev.get("default_password"):
            sec_issues += 3
        if not dev.get("ssh_only"):
            sec_issues += 1
    scores["security"] = max(0, 100 - sec_issues * 4)

    # 综合得分
    total = (
        scores["device_health"] * 0.20 +
        scores["config_compliance"] * 0.25 +
        scores["link_quality"] * 0.15 +
        scores["protocol_status"] * 0.15 +
        scores["security"] * 0.15
    )

    return {
        "dimension_scores": scores,
        "total_score": round(total, 1),
        "rating": get_rating(total)
    }

def get_rating(score):
    if score >= 90: return "优秀"
    if score >= 75: return "良好"
    if score >= 60: return "一般"
    if score >= 40: return "较差"
    return "危险"
4.6 趋势对比分析
# 三次健康检查趋势对比
# 检查时间:2024-Q1 / 2024-Q2 / 2024-Q3

| 维度 | Q1得分 | Q2得分 | Q3得分 | 趋势 |
|------|--------|--------|--------|------|
| 设备健康 | 68 | 72 | 78 | ↗ 持续改善 |
| 配置规范 | 60 | 65 | 75 | ↗ 持续改善 |
| 链路质量 | 75 | 78 | 82 | ↗ 持续改善 |
| 协议状态 | 65 | 70 | 74 | ↗ 持续改善 |
| 安全合规 | 45 | 55 | 70 | ↗ 大幅改善 |
| 文档完整 | 35 | 45 | 60 | ↗ 大幅改善 |
| **综合** | **59.7** | **67.5** | **76.5** | **↗ 良好** |

# Q3相比Q1的主要改善:
# 1. 安全合规:从45→70,修复了所有弱密码和SNMP v2c问题
# 2. 文档完整:从35→60,完成了核心拓扑和IP地址文档补全
# 3. 设备健康:从68→78,更换了故障风扇和高温设备
# 4. 综合等级:从"一般"提升至"良好"
4.7 健康检查报告模板结构
# XX公司网络健康检查报告

## 1. 执行摘要
- 检查时间范围
- 检查设备数量
- 综合评分及等级
- Top 5 风险项

## 2. 详细发现
### 2.1 设备健康
### 2.2 配置规范
### 2.3 链路质量
### 2.4 协议状态
### 2.5 安全合规
### 2.6 文档完整性

## 3. 风险矩阵
(高风险/中风险/低风险分类展示)

## 4. 改进建议
(按优先级排序,含具体操作步骤)

## 5. 附录
- 完整命令输出
- 设备清单
- 拓扑图
4.8 健康检查报告摘要
| 检查维度 | 得分 | 等级 | 主要问题数 |
|---|---|---|---|
| 设备健康 | 72 | 一般 | 8个硬件告警 |
| 配置规范 | 65 | 一般 | 23个配置不规范 |
| 链路质量 | 78 | 良好 | 3个高负载链路 |
| 协议状态 | 70 | 一般 | 5个协议异常 |
| 安全合规 | 55 | 较差 | 12个安全问题 |
| 文档完整 | 45 | 较差 | 拓扑文档缺失 |
综合评分:67.5(一般)
4.9 改进优先级
| 优先级 | 问题 | 修复时间 | 责任人 |
|---|---|---|---|
| P0 | 风扇故障、温度告警 | 立即 | 运维组 |
| P0 | SNMP弱密码、默认社区名 | 24小时内 | 安全组 |
| P1 | OSPF邻居Flapping | 1周内 | 网络组 |
| P1 | 链路高负载 | 2周内 | 网络组 |
| P2 | 文档缺失 | 1月内 | 文档组 |
| P2 | BGP未启用BFD | 2周内 | 网络组 |
五、经验总结
| 序号 | 经验类别 | 经验内容 | 适用场景 |
|---|---|---|---|
| 1 | 定期检查 | 健康检查应至少每季度进行一次 | 运维管理 |
| 2 | 自动化采集 | 使用脚本自动化采集,提高效率 | 自动化 |
| 3 | 评分体系 | 建立量化的评分体系,便于横向对比 | 评估标准 |
| 4 | 优先级分级 | 问题按风险等级分级处理 | 问题管理 |
| 5 | 安全优先 | 安全问题必须优先修复 | 安全管理 |
| 6 | 文档先行 | 健康检查前应要求客户提供现有文档 | 项目管理 |
| 7 | 持续跟踪 | 修复建议必须有跟踪验证机制 | 持续改进 |
| 8 | 基线对比 | 与上次检查结果对比,评估改进趋势 | 趋势分析 |
| 9 | 客户沟通 | 检查过程中保持与客户IT团队的沟通 | 客户服务 |
| 10 | 价值体现 | 健康检查不仅是发现问题,更要提供可执行的改进方案 | 服务价值 |
思考
- 网络健康检查的自动化程度能到什么程度?哪些检查项必须人工完成?
- 如何设计一个持续性的网络健康监控系统,替代周期性的手工健康检查?
- 健康检查发现的安全问题(如弱密码、默认SNMP社区名)为什么在很多网络中长期存在?如何从根本上解决?
下篇预告:第353篇:现网性能瓶颈分析与带宽扩容建议