第350篇:跨厂商设备互联互通排错案例
关键词:跨厂商互联、OSPF、MPLS、LACP、BGP、兼容性
一、案例背景
某跨国企业收购了一家海外公司后,需要将两家的网络进行整合。企业原有网络全为华为设备,被收购方使用Cisco和Juniper设备。在互联互通过程中,多个层面出现了兼容性问题。
网络整合范围: - 华为侧:NE40E(PE)、CE6865(核心)、AR6140(出口) - Cisco侧:ASR9000(PE)、Nexus 9000(核心) - Juniper侧:PTX1000(核心)、MX204(出口)
故障现象: 1. OSPF邻居在华为NE40E和Cisco ASR9000之间无法建立 2. MPLS LDP会话在华为和Juniper之间建立后频繁断开 3. LACP Eth-Trunk在华为CE和Cisco Nexus之间状态异常 4. BGP eBGP会话在华为AR和Juniper MX之间建立但路由未学习
二、需求分析与方案设计
2.1 跨厂商互联常见问题
| 协议 | 常见问题 | 华为 | Cisco | Juniper |
|---|---|---|---|---|
| OSPF | MTU不匹配、认证差异、Option Bits | 默认MTU检测 | 默认不检测MTU | 默认不检测MTU |
| MPLS | Label分配方式、TTL处理方式 | Libera/Per-platform | Per-platform | Per-platform |
| LACP | System ID计算、超时时间 | 基于MAC | 基于优先级+MAC | 基于MAC |
| BGP | GR机制、MD5密钥协商、AS4字节 | 支持4字节AS | 支持4字节AS | 支持4字节AS |
| STP | BPDU格式、优先级计算 | 802.1w(RSTP) | PVST+(私有) | RSS-Bridge |
2.1.1 跨厂商默认参数对照表
| 协议参数 | 华为VRP | Cisco IOS/IOS-XR | Juniper Junos |
|---|---|---|---|
| OSPF Hello Interval | 10s (广播) | 10s | 10s |
| OSPF Dead Interval | 40s | 40s | 40s |
| OSPF MTU检测 | 默认开启(ipo-cpm) | 默认关闭 | 默认关闭 |
| OSPF Router Priority | 1 | 1 | 128 |
| BGP Keepalive | 30s | 60s | 30s |
| BGP Holdtimer | 90s | 180s | 90s |
| LDP Keepalive | 30s | 10s | 60s |
| LACP Timeout | 3s (slow) | 3s (slow) | 3s (slow) |
| STP Priority | 32768 | 32768 | 32768 |
| STP Hello Time | 2s | 2s | 2s |
| Interface MTU | 1500 | 1500 | 1500 |
| Jumbo Frame | 需手动配置 | 需手动配置 | 需手动配置 |
2.2 排错思路
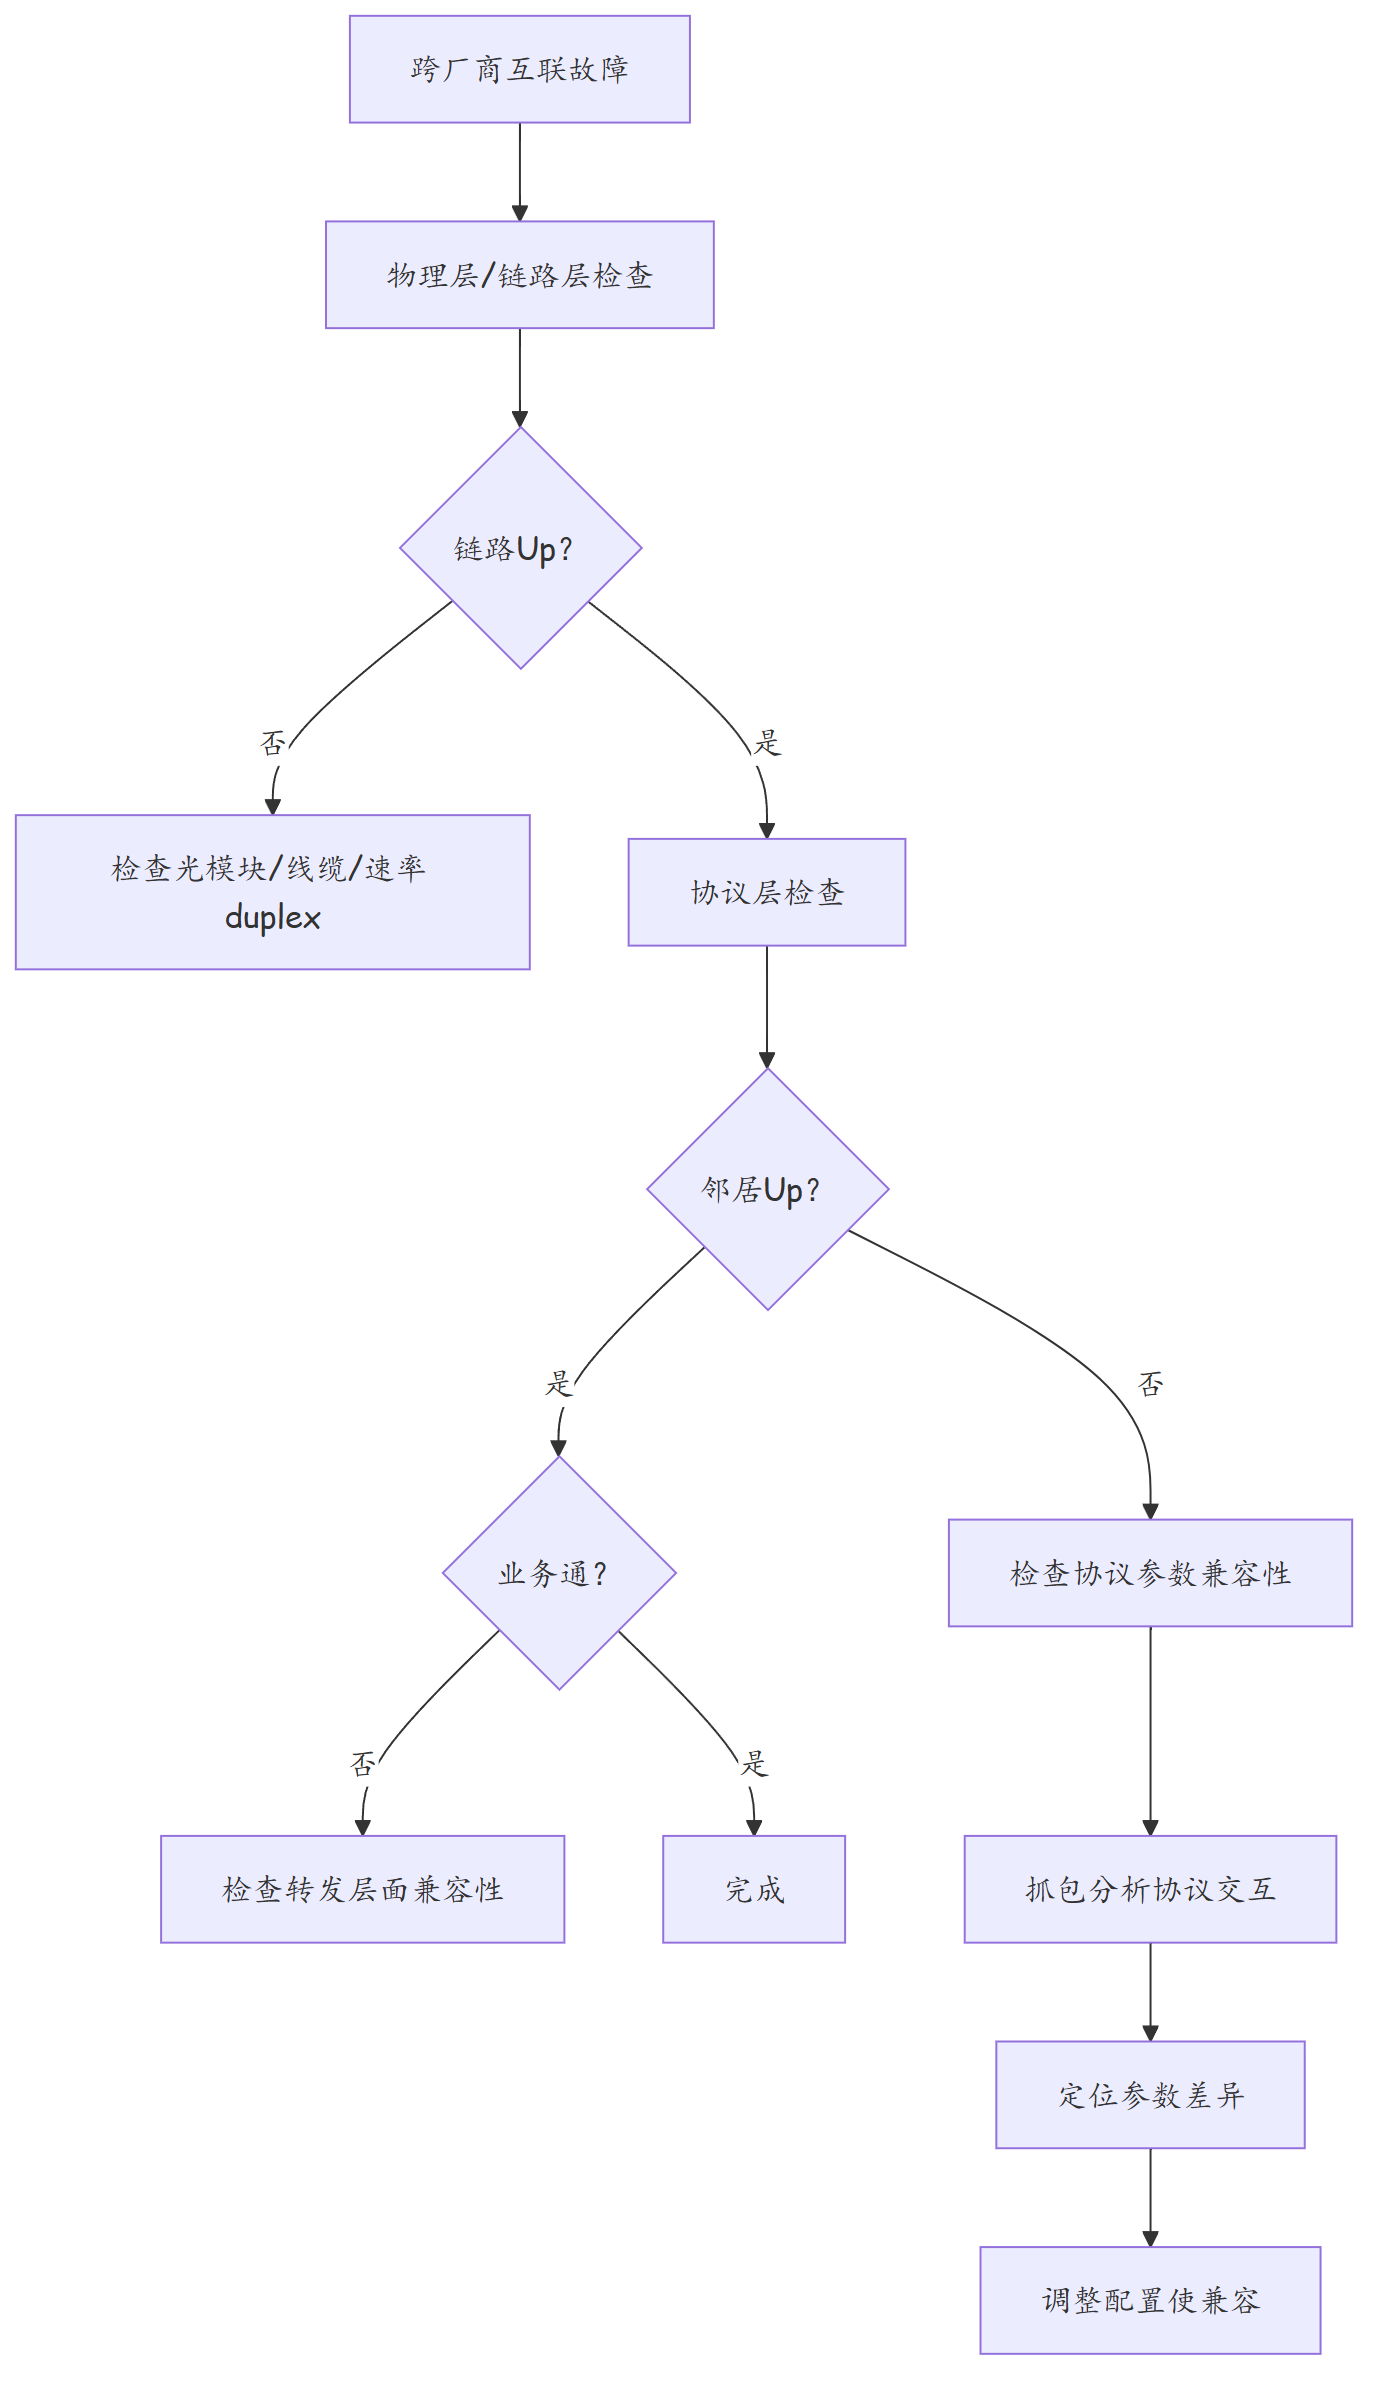
2.3 跨厂商兼容性检查清单
| 检查项 | OSPF | MPLS | LACP | BGP |
|---|---|---|---|---|
| IP连通性 | ✓ | ✓ | ✓ | ✓ |
| MTU匹配 | ✓ | ✓ | - | - |
| 认证方式 | ✓ | - | - | ✓ |
| Timer匹配 | ✓ | ✓ | ✓ | ✓ |
| 版本一致 | ✓ | - | ✓ | ✓ |
| 系统ID/优先级 | - | - | ✓ | - |
| Hello/Kill Interval | ✓ | ✓ | ✓ | ✓ |
三、技术细节与实施过程
3.1 OSPF邻居无法建立
故障现象:华为NE40E与Cisco ASR9000的OSPF邻居始终停留在INIT状态。
# 华为侧OSPF状态
<NE40E> display ospf peer
OSPF Process 1 with Router ID 10.1.1.1
Neighbor:
  Address         State     Pri   DeadTimer   RouterID        Interface
  10.0.0.2        Init      1     35          10.2.2.2        GE0/0/1

# Cisco侧OSPF状态
ASR9000# show ip ospf neighbor
Neighbor ID   Pri   State           Dead Time   Address         Interface
10.1.1.1      1     INIT            00:00:33    10.0.0.1        Gi0/0/0
根因分析: 1. 抓包发现华为发送的OSPF Hello包中MTU字段为1500,Cisco侧接口MTU为9000(Jumbo Frame) 2. 华为OSPF默认启用MTU检测(ipo-cpm-enable),收到MTU不匹配的Hello包后不前进到2-Way状态
# 解决方案:在华为侧关闭OSPF MTU检测
<NE40E> system-view
[NE40E] ospf 1
[NE40E-ospf-1] area 0
[NE40E-ospf-1-area-0.0.0.0] interface GigabitEthernet 0/0/1
[NE40E-ospf-1-area-0.0.0.0-if-GigabitEthernet0/0/1] undo ipo-cpm-enable
[NE40E-ospf-1-area-0.0.0.0-if-GigabitEthernet0/0/1] quit
[NE40E-ospf-1-area-0.0.0.0] quit
[NE40E-ospf-1] quit

# 验证OSPF邻居
<NE40E> display ospf peer
Neighbor:
  Address         State     Pri   DeadTimer   RouterID        Interface
  10.0.0.2        Full      1     35          10.2.2.2        GE0/0/1  <-- Full状态
3.2 MPLS LDP频繁断开
故障现象:华为NE40E与Juniper PTX1000的LDP会话建立后,每30分钟左右断开一次。
# 华为侧LDP状态
<NE40E> display mpls ldp peer
Peer Status:
  Peer-Address    State     LDP-ID     KeepAlive
  10.0.1.2        Operative 0.0.0.0:0:0  Hold:8 Init:30

# LDP日志
*Mar 15 10:30:00 NE40E LDP: LDP session with 10.0.1.2 down, reason: Keepalive timeout
*Mar 15 10:30:05 NE40E LDP: LDP session with 10.0.1.2 up
根因:华为LDP默认KeepAlive为30秒,Juniper默认为60秒。华为在30秒后未收到Juniper的KeepAlive报文,判定对端Down。
# 方案1:在华为侧调整LDP KeepAlive匹配Juniper
[NE40E] mpls ldp
[NE40E-ldp] keepalive 60  # 匹配Juniper的60秒
[NE40E-ldp] hold 180       # Hold时间为KeepAlive的3倍
[NE40E-ldp] quit

# 方案2:在Juniper侧调整匹配华为
# set protocols mpls ldp interface all hello interval 10
# set protocols mpls ldp interface all hello hold-time 30
3.3 LACP Eth-Trunk异常
故障现象:华为CE6865与Cisco Nexus 9000之间的LACP Eth-Trunk只有1条成员链路Active。
# 华为侧Eth-Trunk状态
<CE6865> display eth-trunk 10
Eth-Trunk10 is up
  Member: 100GE1/0/1  up    LACP
  Member: 100GE1/0/2  down  LACP  <-- 第二条链路Down

# Cisco侧Port-Channel状态
Nexus9000# show lacp summary
Port-channel: Po10
  Age   Sum   Ports   Protocol
  01:23 0x00001 1     LACP
根因:华为LACP System ID使用MAC地址计算,Cisco使用优先级+MAC。当优先级不同时,LACP协商的Actor System ID不同,导致部分链路无法加入。
# 解决方案:统一LACP System Priority
# 华为侧
[CE6865] interface Eth-Trunk 10
[CE6865-Eth-Trunk10] lacp system-priority 32768
[CE6865-Eth-Trunk10] quit

# Cisco侧
Nexus9000# configure terminal
Nexus9000(config)# interface port-channel 10
Nexus9000(config-if)# lacp system-priority 32768
Nexus9000(config-if)# exit
3.4 BGP路由未学习
故障现象:华为AR6140与Juniper MX204的BGP eBGP会话Up,但华为侧没有学到Juniper发布的路由。
# 华为侧BGP状态
<AR6140> display bgp peer
IPv4 Session:
  BGP peer is 203.0.113.1
  GracefulRestart: Not configured
  State: Established
  Message statistics:
    UpdRec: 1    UpdSent: 1
    UpdPrefixRec: 0    <-- 前缀接收为0!

# Juniper侧BGP状态
MX204> show bgp summary
Peer            AS  InPkt  OutPkt  OutQ  UPtime  State     InAct  OutAct
203.0.113.254  65001  1234    567     0  01:23:45 Estab       5        0
根因:Juniper默认启用BGP Graceful Restart,华为侧未启用。Juniper在GR期间不发送路由更新,华为侧收不到路由。
# 华为侧启用BGP Graceful Restart
[AR6140] bgp 65001
[AR6140-bgp-65001] graceful-restart
[AR6140-bgp-65001] peer 203.0.113.1 graceful-restart
[AR6140-bgp-65001] quit

# 验证路由学习
<AR6140> display bgp routing-table peer 203.0.113.1
Network          NextHop         MED      LocPrf    Path/Ogn
*> 10.10.0.0/16   203.0.113.1     0        100      65002?i  <-- 路由已学习
3.5 BGP MD5认证跨厂商兼容性
故障现象:华为与Cisco之间配置了BGP MD5认证,但会话反复在OpenSent和Established之间震荡。
# 华为侧日志
*Mar 15 11:00:00 AR6140 BGP: %BGP-5-ADJCHG: Peer 203.0.113.1 Down, TCP connection reset
*Mar 15 11:00:05 AR6140 BGP: %BGP-5-ADJCHG: Peer 203.0.113.1 Up

# 根因:华为使用TCP MD5 Signature (RFC 2385),
# Cisco IOS-XR支持TCP-AO (RFC 5925) 和 TCP MD5,
# 但默认可能优先尝试TCP-AO,导致协商失败
解决方案:
# 华为侧:确认使用TCP MD5
[AR6140] bgp 65001
[AR6140-bgp-65001] peer 203.0.113.1 tcp-md5-key Huawei@2024

# Cisco IOS-XR侧:显式配置TCP MD5(非TCP-AO)
RP/0/RP0/CPU0:ASR9K# configure terminal
ASR9K(config)# router bgp 65002
ASR9K(config-router)# neighbor 203.0.113.254 tcp-md5-signature key-string Huawei@2024
ASR9K(config-router)# ^Z

# 验证:两端BGP日志确认MD5协商成功
<AR6140> display bgp peer 203.0.113.1
TCP-MD5-KEY: Huawei@2024  <-- 确认MD5生效
3.6 STP跨厂商兼容性
故障现象:华为CE6865与Cisco Nexus 9000之间运行STP,但Cisco侧始终选举自己为根桥,导致流量绕行。
# 华为侧STP
<CE6865> display stp brief
MSTID  Port            Role  STP State  Protection
0      XGig1/0/1       Desi  FORWARDING  NONE

# Cisco侧STP
Nexus9000# show spanning-tree
Legend: ...
Root ID    Priority    32768
           Address     xxxx.xxxx.xxxx
           This bridge is the root  <-- Cisco认为自己是根桥
根因:华为运行标准802.1w RSTP,Cisco Nexus默认运行PVST+(每VLAN生成树)。BPDU格式不同,导致根桥计算不一致。
解决方案:
# 方案1:统一使用MSTP(推荐)
# 华为侧
[CE6865] stp mode mstp
[CE6865] stp region-configuration
[CE6865-mstp-region] region-name DC-REGION
[CE6865-mstp-region] revision-level 1
[CE6865-mstp-region] instance 1 vlan 10-20
[CE6865-mstp-region] active region-configuration
[CE6865-mstp-region] quit
[CE6865] stp priority 0  # 华为作为根桥

# Cisco Nexus侧
Nexus9000# configure terminal
Nexus9000(config)# spanning-tree mode mst
Nexus9000(config)# spanning-tree mst configuration
Nexus9000(config-mst)# name DC-REGION
Nexus9000(config-mst)# revision 1
Nexus9000(config-mst)# instance 1 vlan 10-20
Nexus9000(config-mst)# exit
Nexus9000(config)# spanning-tree mst 1 priority 4096  # Cisco作为备用根桥
跨厂商STP兼容性对照:
| 特性 | 华为(RSTP/MSTP) | Cisco(PVST+/MST) | Juniper(RSTP/MST) |
|---|---|---|---|
| BPDU类型 | 802.1w | 0x2000(私有)/802.1w | 802.1w |
| 优先级步进 | 4096 | 4096 | 4096 |
| 默认优先级 | 32768 | 32768 | 32768 |
| Hello Time | 2s | 2s | 2s |
| Forward Delay | 15s | 15s | 15s |
| 兼容建议 | MSTP模式+统一Region | MSTP模式+统一Region | MSTP模式+统一Region |
四、实战配置/案例分析
4.1 跨厂商互联配置模板
# ========== 华为OSPF与Cisco互联 ==========
# 华为侧
[NE40E] ospf 1
[NE40E-ospf-1] area 0
[NE40E-ospf-1-area-0.0.0.0] interface GigabitEthernet 0/0/1
[NE40E-ospf-1-area-0.0.0.0-if-GigabitEthernet0/0/1] undo ipo-cpm-enable  # 关闭MTU检测
[NE40E-ospf-1-area-0.0.0.0-if-GigabitEthernet0/0/1] timer spf 50 500 5000  # 调整SPF定时器
[NE40E-ospf-1-area-0.0.0.0-if-GigabitEthernet0/0/1] quit

# ========== 华为MPLS与Juniper互联 ==========
[NE40E] mpls ldp
[NE40E-ldp] keepalive 60    # 匹配对端KeepAlive
[NE40E-ldp] hold 180
[NE40E-ldp] router-id 10.1.1.1  # 显式指定Router ID
[NE40E-ldp] quit

# ========== 华为LACP与Cisco互联 ==========
[CE6865] interface Eth-Trunk 10
[CE6865-Eth-Trunk10] mode lacp-static
[CE6865-Eth-Trunk10] lacp system-priority 32768
[CE6865-Eth-Trunk10] lacp period fast  # 快速LACP(可选)
[CE6865-Eth-Trunk10] quit
4.2 跨厂商兼容性测试报告
| 互联类型 | 测试项 | 结果 | 备注 |
|---|---|---|---|
| 华为↔Cisco OSPF | 邻居建立 | ✓ | 关闭MTU检测 |
| 华为↔Cisco OSPF | 路由学习 | ✓ | 正常 |
| 华为↔Juniper MPLS | LDP会话 | ✓ | 调整KeepAlive |
| 华为↔Juniper MPLS | Label分发 | ✓ | 正常 |
| 华为↔Cisco LACP | Eth-Trunk | ✓ | 统一System Priority |
| 华为↔Juniper BGP | 会话建立 | ✓ | 启用GR |
| 华为↔Juniper BGP | 路由学习 | ✓ | 正常 |
| 华为↔Cisco STP | 根桥选举 | ✓ | 统一MSTP+Region |
4.3 跨厂商排错标准流程
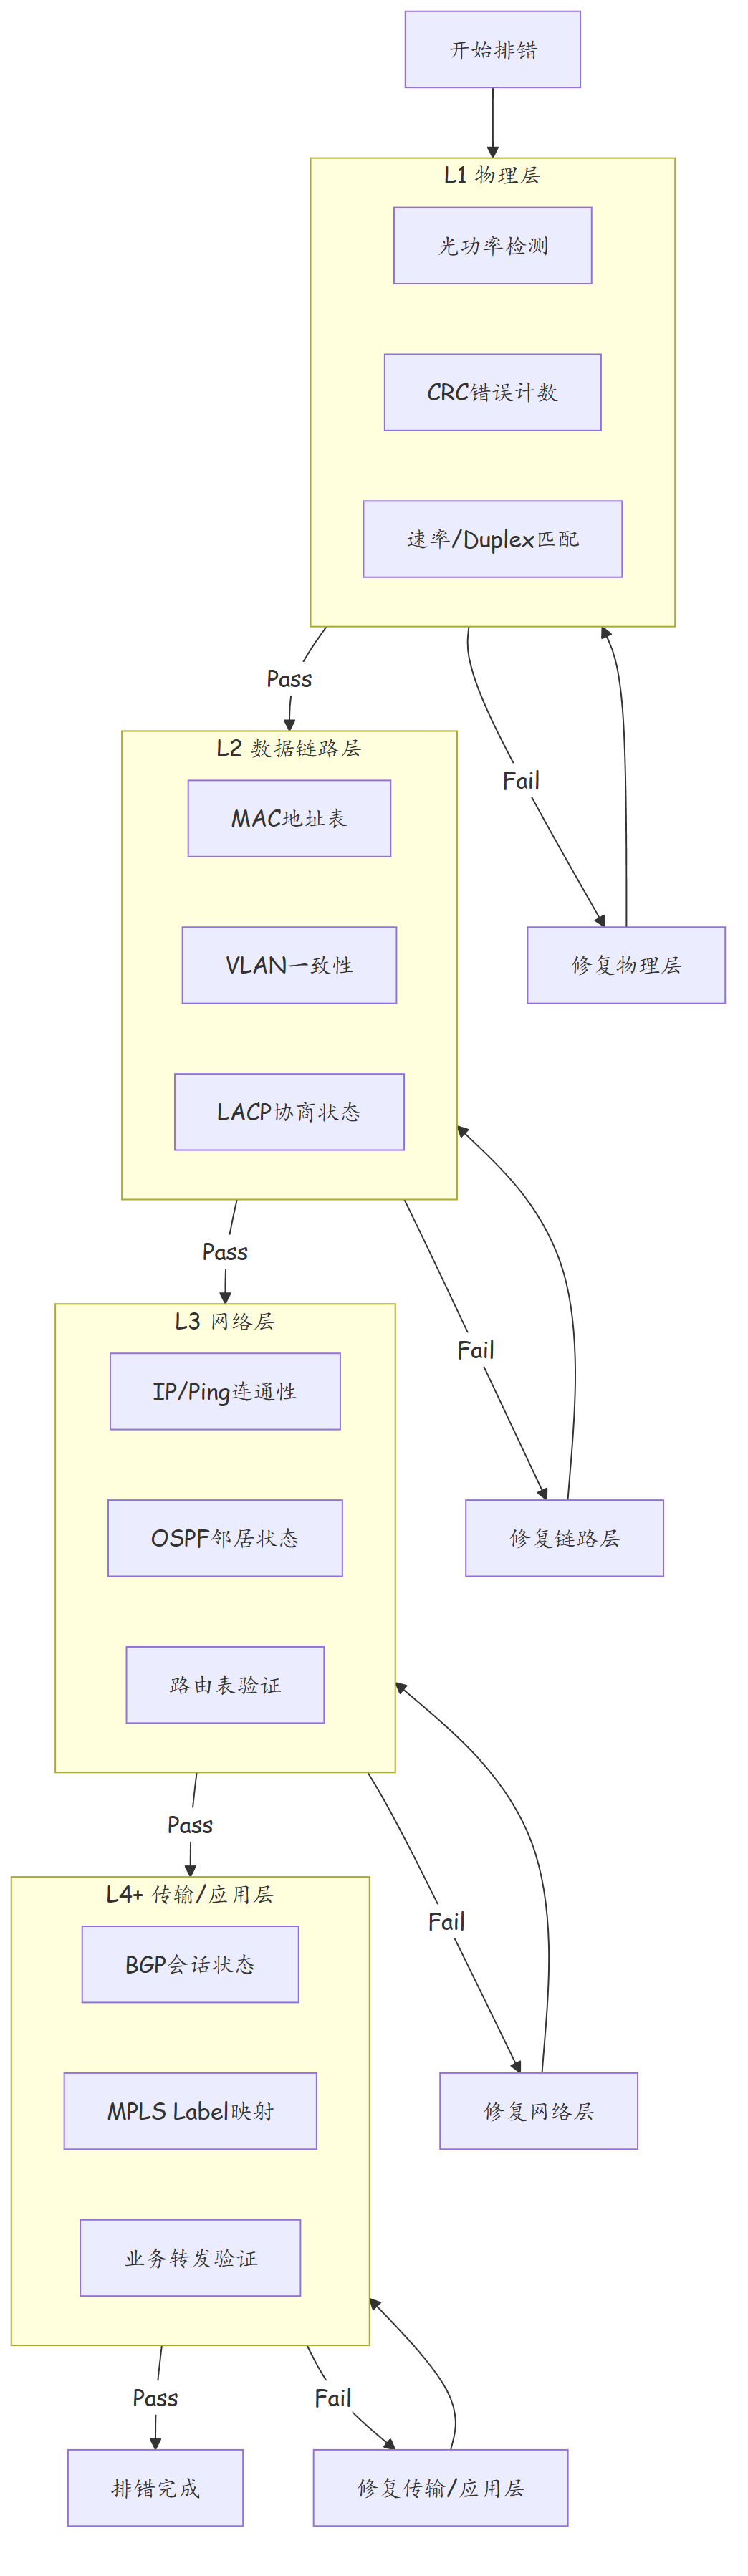
4.4 跨厂商互联预测试Checklist
| 序号 | 检查项 | OSPF | MPLS | LACP | BGP | STP |
|---|---|---|---|---|---|---|
| 1 | 接口物理状态 | ✓ | ✓ | ✓ | ✓ | ✓ |
| 2 | IP地址/子网 | ✓ | ✓ | - | ✓ | - |
| 3 | MTU匹配 | ✓ | ✓ | - | - | - |
| 4 | VLAN/Trunk配置 | - | - | ✓ | - | ✓ |
| 5 | 协议Area/AS | ✓ | - | - | ✓ | - |
| 6 | Hello/Dead Timer | ✓ | - | - | ✓ | - |
| 7 | KeepAlive/Hold | - | ✓ | ✓ | ✓ | - |
| 8 | 认证(密码/算法) | ✓ | - | - | ✓ | - |
| 9 | Priority匹配 | ✓ | - | ✓ | - | ✓ |
| 10 | GR机制 | - | - | - | ✓ | - |
| 11 | 抓包验证协议交互 | ✓ | ✓ | ✓ | ✓ | ✓ |
四、实战工具与自动化排错
4.5 Python多厂商设备配置比对工具
跨厂商排错的核心是快速发现参数差异。下面提供一套基于Netmiko的配置比对工具,支持华为/Cisco/Juniper三厂商。
#!/usr/bin/env python3
"""
跨厂商设备配置比对工具 - MultiVendor Config Comparator
支持华为VRP / Cisco IOS-XR / Juniper Junos 关键参数提取与差异报告生成
"""
from netmiko import ConnectHandler
import json
import sys
from datetime import datetime

DEVICE_TYPES = {
    'huawei': 'huawei_vrpv8',
    'cisco': 'cisco_xr',
    'juniper': 'juniper_junos'
}

# 各厂商OSPF关键参数提取命令映射
OSPF_COMMANDS = {
    'huawei': [
        ('display ospf interface', 'ospf_interfaces'),
        ('display ospf peer', 'ospf_peers'),
        ('display current-configuration configuration ospf', 'ospf_config'),
    ],
    'cisco': [
        ('show ip ospf interface', 'ospf_interfaces'),
        ('show ip ospf neighbor', 'ospf_neighbors'),
        ('show running-config router ospf', 'ospf_config'),
    ],
    'juniper': [
        ('show ospf interface', 'ospf_interfaces'),
        ('show ospf neighbor', 'ospf_neighbors'),
        ('show configuration protocols ospf', 'ospf_config'),
    ],
}

# 各厂商BGP关键参数提取命令映射
BGP_COMMANDS = {
    'huawei': [
        ('display bgp peer', 'bgp_peers'),
        ('display current-configuration configuration bgp', 'bgp_config'),
    ],
    'cisco': [
        ('show bgp summary', 'bgp_peers'),
        ('show running-config router bgp', 'bgp_config'),
    ],
    'juniper': [
        ('show bgp summary', 'bgp_peers'),
        ('show configuration protocols bgp', 'bgp_config'),
    ],
}


class DeviceConnector:
    """多厂商设备连接封装"""
    def __init__(self, host, vendor, username='admin', password=''):
        self.host = host
        self.vendor = vendor
        self.device = {
            'device_type': DEVICE_TYPES[vendor],
            'host': host,
            'username': username,
            'password': password,
            'session_log': f'{host}_session.log'
        }

    def connect(self):
        self.conn = ConnectHandler(**self.device)
        return self.conn

    def execute(self, command):
        return self.conn.send_command(command, use_textfsm=False)


def extract_params(device_info, protocol='ospf'):
    """提取设备协议参数"""
    host, vendor, username, password = device_info
    connector = DeviceConnector(host, vendor, username, password)
    connector.connect()

    commands = OSPF_COMMANDS if protocol == 'ospf' else BGP_COMMANDS
    vendor_commands = commands.get(vendor, [])
    result = {'host': host, 'vendor': vendor, 'protocol': protocol,
              'timestamp': datetime.now().isoformat()}

    for cmd, key in vendor_commands:
        try:
            output = connector.execute(cmd)
            result[key] = output
        except Exception as e:
            result[key] = f'ERROR: {e}'

    return result


def compare_ospf_params(device_a, device_b):
    """比对两台设备的OSPF参数差异"""
    differences = []

    # MTU检测差异
    if 'huawei' in [device_a['vendor'], device_b['vendor']]:
        differences.append({
            'param': 'OSPF MTU检测(ipo-cpm)',
            'device_a': '默认开启' if device_a['vendor'] == 'huawei' else '默认关闭',
            'device_b': '默认开启' if device_b['vendor'] == 'huawei' else '默认关闭',
            'risk': 'HIGH' if device_a['vendor'] != device_b['vendor'] else 'LOW',
            'recommendation': '华为侧关闭ipo-cpm-enable,或统一两端MTU'
        })

    # Router Priority差异
    priorities = {'huawei': 1, 'cisco': 1, 'juniper': 128}
    differences.append({
        'param': 'OSPF Router Priority',
        'device_a': f"{device_a['vendor']}: {priorities.get(device_a['vendor'], 1)}",
        'device_b': f"{device_b['vendor']}: {priorities.get(device_b['vendor'], 1)}",
        'risk': 'MEDIUM',
        'recommendation': '如需指定DR/BDR,手动统一两端Priority'
    })

    return differences


def compare_bgp_params(device_a, device_b):
    """比对两台设备的BGP参数差异"""
    differences = []

    timers = {
        'huawei': {'keepalive': '30s', 'holdtimer': '90s'},
        'cisco': {'keepalive': '60s', 'holdtimer': '180s'},
        'juniper': {'keepalive': '30s', 'holdtimer': '90s'}
    }

    for timer_name in ['keepalive', 'holdtimer']:
        differences.append({
            'param': f'BGP {timer_name}',
            'device_a': f"{device_a['vendor']}: {timers[device_a['vendor']][timer_name]}",
            'device_b': f"{device_b['vendor']}: {timers[device_b['vendor']][timer_name]}",
            'risk': 'HIGH' if timers[device_a['vendor']][timer_name] != timers[device_b['vendor']][timer_name] else 'LOW',
            'recommendation': '统一两端定时器或使用 negotiate-auto'
        })

    # GR差异
    differences.append({
        'param': 'BGP Graceful Restart',
        'device_a': f"{device_a['vendor']}: 需手动配置",
        'device_b': f"{device_b['vendor']}: 需手动配置(Juniper默认启用)",
        'risk': 'MEDIUM',
        'recommendation': '两端同时启用GR,Juniper默认启用需注意'
    })

    return differences


def generate_report(differences, output_file='diff_report.json'):
    """生成差异报告"""
    report = {
        'report_time': datetime.now().isoformat(),
        'total_issues': len(differences),
        'high_risk': sum(1 for d in differences if d['risk'] == 'HIGH'),
        'medium_risk': sum(1 for d in differences if d['risk'] == 'MEDIUM'),
        'low_risk': sum(1 for d in differences if d['risk'] == 'LOW'),
        'differences': differences
    }
    with open(output_file, 'w', encoding='utf-8') as f:
        json.dump(report, f, indent=2, ensure_ascii=False)
    return report


# 使用示例:比对华为↔Cisco OSPF参数
if __name__ == '__main__':
    dev_a = {'host': '10.0.0.1', 'vendor': 'huawei'}
    dev_b = {'host': '10.0.0.2', 'vendor': 'cisco'}

    diffs = compare_ospf_params(dev_a, dev_b)
    diffs.extend(compare_bgp_params(dev_a, dev_b))

    report = generate_report(diffs)
    print(f"差异报告已生成: HIGH={report['high_risk']}, "
          f"MEDIUM={report['medium_risk']}, LOW={report['low_risk']}")
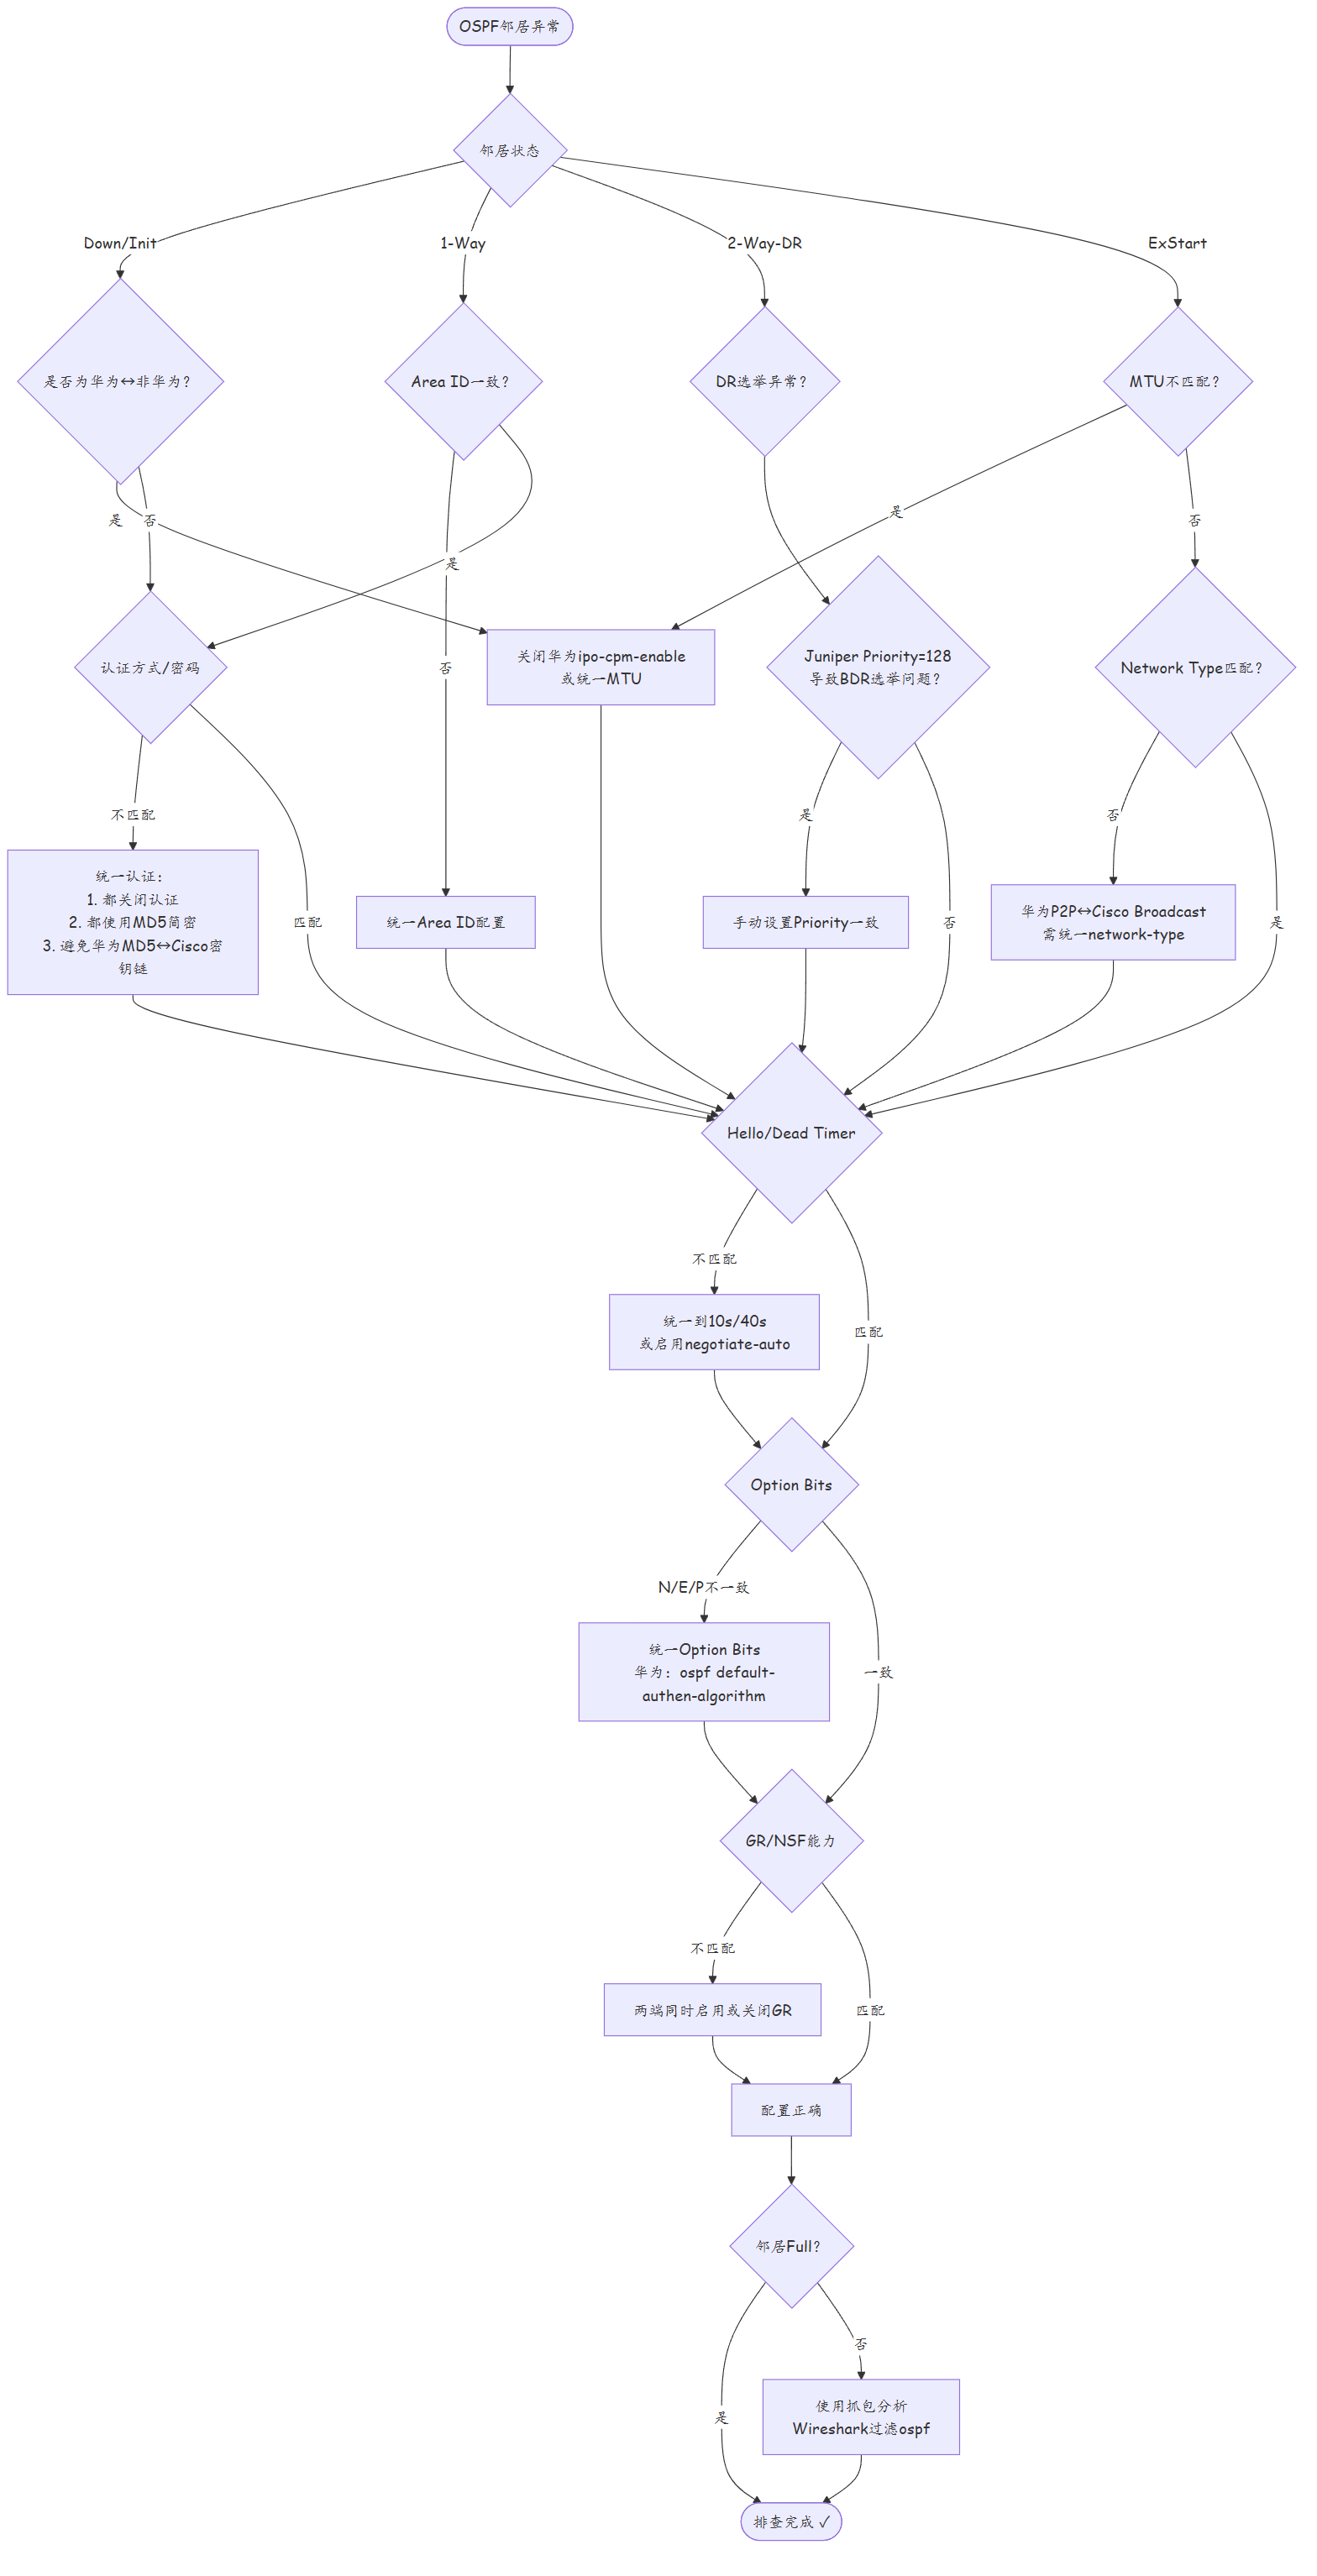
4.6 多厂商OSPF邻居故障排查流程图
当跨厂商OSPF邻居无法建立时,按以下流程图系统化排查:
4.7 BGP MD5认证跨厂商兼容性详解
BGP MD5认证在跨厂商场景中最容易出现兼容性问题。以下是各厂商实现差异的完整对照:
| 维度 | 华为VRP | Cisco IOS-XR | Cisco IOS (NX-OS) | Juniper Junos | H3C Comware |
|---|---|---|---|---|---|
| 标准支持 | RFC 2385 TCP-MD5 | RFC 2385 + RFC 5925(TCP-AO) | RFC 2385 | RFC 2385 | RFC 2385 |
| TCP-AO支持 | 部分版本支持 | 默认支持 | 不支持 | 不支持 | 不支持 |
| 密钥长度 | 8-127字符 | 8-127字符 | 8-127字符 | 8-127字符 | 4-127字符 |
| 密钥变更方式 | 实时生效 | 需要reload BGP会话 | 实时生效 | 需要clear session | 实时生效 |
| 配置关键字 | tcp-md5-key |
tcp-md5-signature |
md5-string |
authentication-key |
tcp-md5-key |
| 多密钥支持 | 不支持 | 支持(key-id) | 不支持 | 不支持 | 不支持 |
常见跨厂商BGP MD5故障及解决:
# 场景1:华为↔Cisco IOS-XR
# 问题:Cisco IOS-XR默认偏好TCP-AO而非TCP-MD5,导致协商失败
# 解决:在Cisco侧显式指定使用TCP-MD5

# Cisco IOS-XR配置
RP/0/RP0/CPU0:ASR9K# configure terminal
ASR9K(config)# router bgp 65002
ASR9K(config-router)# neighbor 203.0.113.254
ASR9K(config-router-subif)# tcp-md5-signature key-string MySecureKey123
# 关键:确保不使用tcp-auth-key(TCP-AO专用)
ASR9K(config-router-subif)# exit

# 华为配置
[Huawei] bgp 65001
[Huawei-bgp-65001] peer 203.0.113.1 tcp-md5-key MySecureKey123

# 场景2:密钥变更时的会话保持
# 问题:修改MD5密钥时BGP会话中断
# 解决:先添加新密钥,再删除旧密钥(部分设备支持)

# 华为侧:直接修改,会话会短暂中断后自动恢复
[Huawei] bgp 65001
[Huawei-bgp-65001] peer 203.0.113.1 tcp-md5-key NewSecureKey456

# 建议操作顺序:
# 1. 先在两端都配置新密钥
# 2. 手动重启一端BGP会话(clear bgp peer x.x.x.x)
# 3. 确认会话Up后再确认
4.8 跨厂商H3C设备互联补充
H3C Comware与华为VRP在命令行上相似,但协议实现仍有差异:
| 差异项 | 华为VRP | H3C Comware | 兼容建议 |
|---|---|---|---|
| OSPF MTU检测 | ipo-cpm-enable |
ospf mtu-enable |
命令不同但行为一致 |
| Eth-Trunk模式 | mode lacp-static |
mode dynamic |
H3C使用dynamic表示LACP |
| VRRP优先级 | vrrp vrid 1 priority 100 |
vrrp vrid 1 virtual-ip x.x.x.x priority 100 |
H3C必须在vrrp下配置虚拟IP |
| 路由策略 | route-policy |
route-policy |
语法基本一致 |
| ACL编号 | 基本ACL: 2000-2999 | 基本ACL: 2000-2999 | 一致 |
五、经验总结
| 序号 | 经验类别 | 经验内容 | 适用场景 |
|---|---|---|---|
| 1 | MTU匹配 | 跨厂商OSPF互联必须注意MTU检测的差异 | OSPF互联 |
| 2 | Timer匹配 | LDP/BGP/STP的定时器必须匹配对端 | 协议互联 |
| 3 | LACP兼容 | LACP System ID计算方式因厂商而异,必须统一优先级 | Eth-Trunk |
| 4 | GR机制 | BGP GR必须在两端同时启用 | BGP互联 |
| 5 | 抓包分析 | 跨厂商排错必须使用抓包分析协议交互 | 故障排查 |
| 6 | 参数文档 | 建立跨厂商参数对照表,减少排错时间 | 文档管理 |
| 7 | 预测试 | 跨厂商互联前必须在实验室预测试 | 变更管理 |
| 8 | 默认值差异 | 不同厂商的默认参数差异很大,不能假设一致 | 协议配置 |
| 9 | 认证兼容 | 跨厂商认证的算法和密钥格式必须兼容 | 安全互联 |
| 10 | 版本差异 | 不同版本的协议实现可能有差异,需注意版本兼容性 | 版本管理 |
思考
- 跨厂商OSPF互联时,除了MTU检测,还有哪些参数差异可能导致邻居无法建立?
- 如果需要在华为、Cisco、Juniper三厂商设备间运行MPLS TE,需要注意哪些兼容性问题?
- 跨厂商网络整合项目中,是否有工具可以自动检测配置兼容性?
下篇预告:第351篇:网络割接回滚方案与应急演练