第169篇:MPLS L2VPN 基础:VPWS 伪线仿真
关键词:L2VPN、VPWS、伪线、PWE3、伪线端点、PW标签、二层仿真
一、引言
MPLS L2VPN(Layer 2 Virtual Private Network)的核心目标是在 MPLS 骨干网上透明地传输二层帧。与 L3VPN 终结三层报文不同,L2VPN 需要在 PE 设备上终结二层帧,通过 MPLS 隧道在 PE 之间传输,再在对端重新封装为二层帧。VPWS(Virtual Private Wire Service,虚拟专用专线服务)是 L2VPN 中最基本的形式,它提供点到点的二层链路仿真。
二、核心概念
2.1 L2VPN 与 L3VPN 对比
| 维度 | L3VPN | L2VPN |
|---|---|---|
| 终结层级 | PE 终结三层 IP 报文 | PE 终结二层帧 |
| 路由处理 | PE 执行路由查找和转发 | PE 不查看二层内容,透明传输 |
| 客户感知 | CE 运行三层协议 | CE unaware of MPLS,如同直连 |
| 标签机制 | 双层标签(公网+VPN) | 双层标签(公网+PW) |
| 典型应用 | 企业广域网互联 | ATM/帧中继仿真、以太网专线 |
2.2 VPWS(Virtual Private Wire Service)
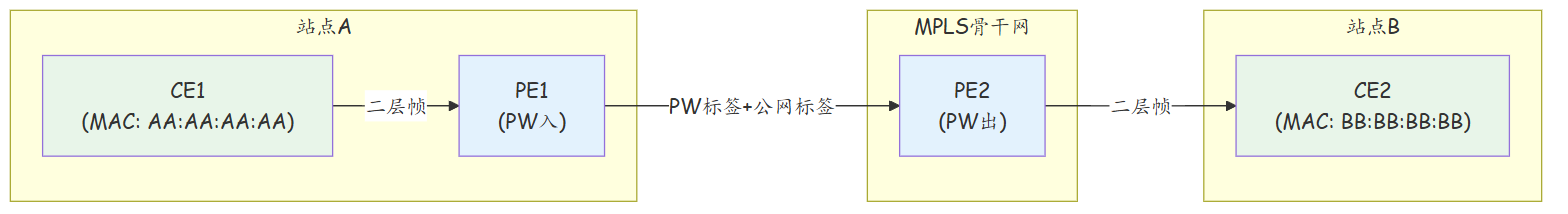
VPWS 通过"伪线"(Pseudowire,PW)在两个 PE 之间仿真一条点到点的二层链路:
2.3 PWE3(Pseudowire Emulation Edge-to-Edge)
PWE3 是 IETF 定义的伪线仿真标准(RFC 4447),规定了 PW 的信令、封装和控制机制:
| 组件 | 说明 |
|---|---|
| CE | Customer Edge,二层客户设备 |
| PW | Pseudowire,PE 之间的逻辑二层通道 |
| PW-TE | Pseudowire Tunnel Endpoint,PE 上 PW 的端点 |
| Control Word | 32位控制字,用于序列号和长度标识 |
2.4 PW 标签与数据封装
| 字段 | 长度 | 说明 |
|---|---|---|
| 公网 LDP 标签 | 32位 | PE 之间的传输路径 |
| PW 标签 | 32位 | 标识 PW 实例(内层标签) |
| Control Word | 32位 | 可选,用于序列号和分片重组 |
| 客户数据 | 可变 | 原始二层帧(Ethernet/ATM/FR) |
三、技术细节
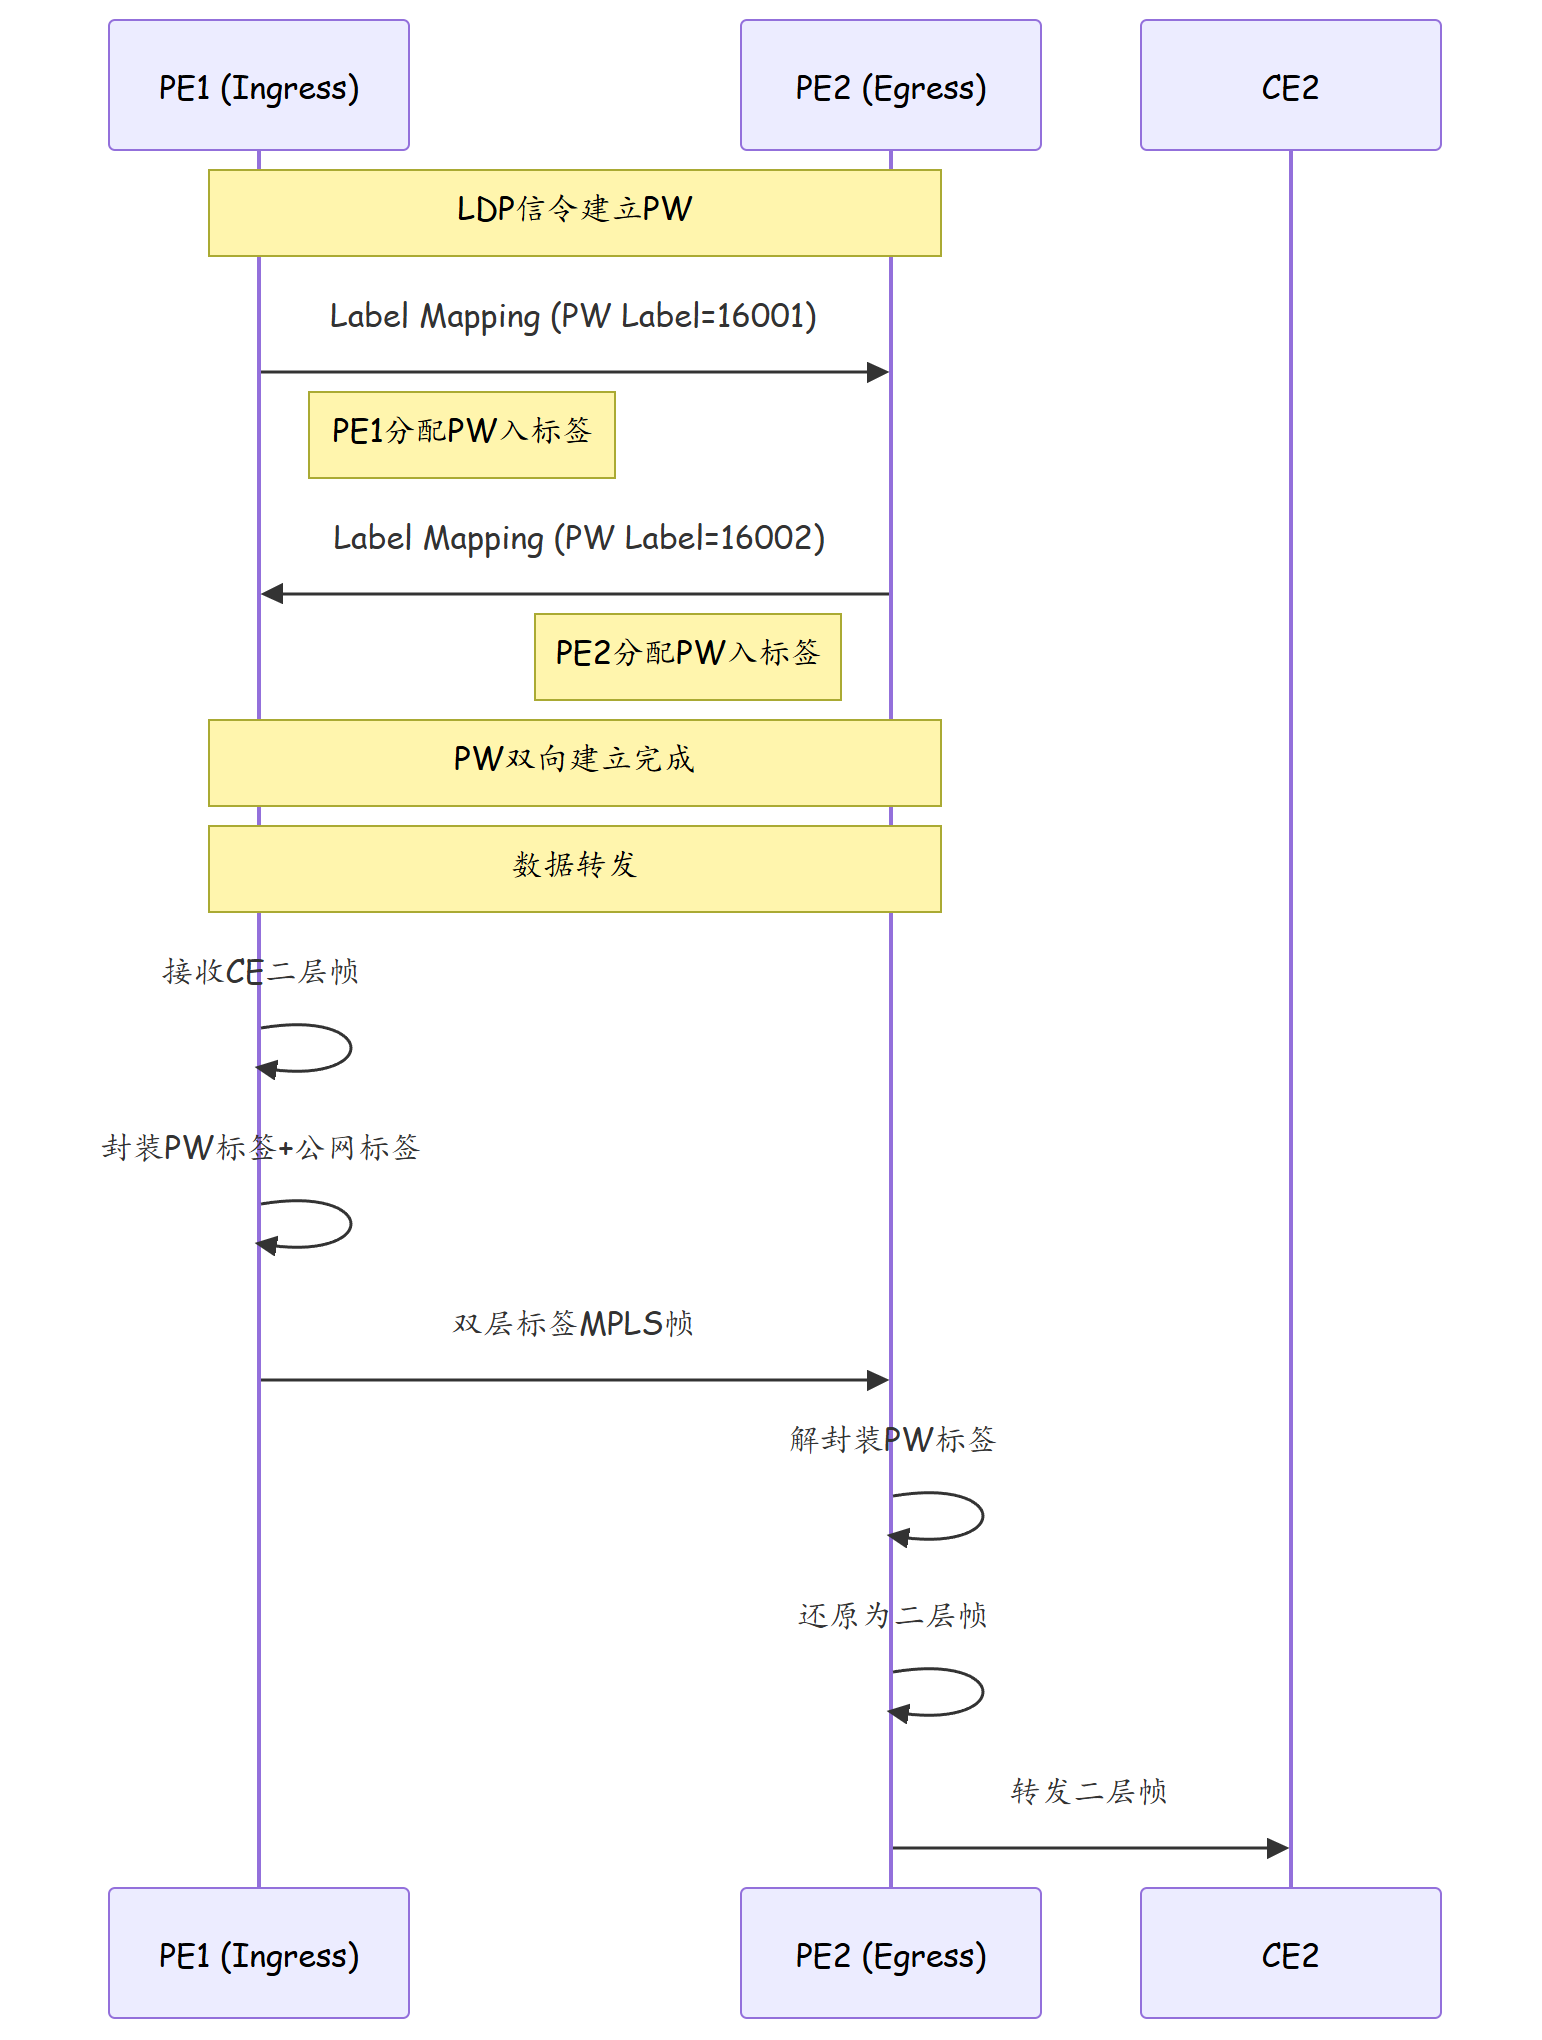
3.1 PW 建立流程
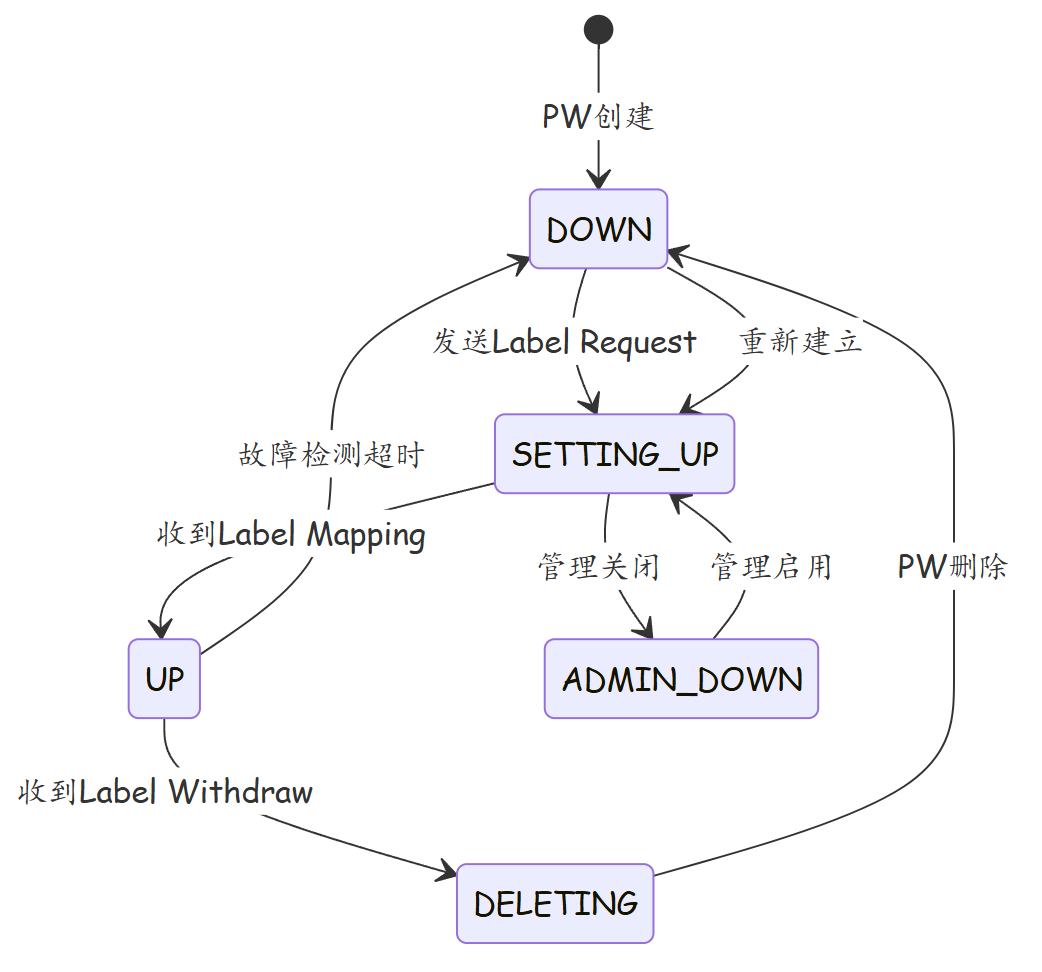
3.2 PW 状态机
3.3 PW 封装类型
| 客户类型 | 封装方式 | Control Word |
|---|---|---|
| Ethernet | 直接封装以太网帧 | 推荐启用 |
| ATM (AAL5) | ATM 适配层 5 | 推荐启用 |
| Frame Relay | Frame Relay 帧 | 推荐启用 |
| PPP | PPP 帧 | 可选 |
Control Word 的作用: - 提供序列号(防止报文乱序) - 标识报文长度(防止 TCP 小分片问题) - 区分不同的 PW 业务类型
3.4 PW 冗余与备份
| 模式 | 说明 |
|---|---|
| 1:1 保护 | 主 PW + 备 PW,故障时切换 |
| 1+1 保护 | 两端同时发送,选择最优接收 |
| 自动重新路由 | PW 故障后自动重建 |
四、实战配置/案例分析
4.1 华为 VPWS 配置
# ========== PE1 配置 ==========
[PE1] interface Bridge 1
[PE1-Bridge1] port gigabitethernet 1/0/0 1
  # 将CE接口加入Bridge域

# 创建PW
[PE1] pw-template VPWS-TPL1
[PE1-pw-template-VPWS-TPL1] pw-type vlan
[PE1-pw-template-VPWS-TPL1] control-word
[PE1-pw-template-VPWS-TPL1] ipv4 10.1.2.1 32
  # 对端PE的LoopBack地址
[PE1-pw-template-VPWS-TPL1] vc-id 100
  # VC ID (伪线标识)

# 绑定PW到Bridge域
[PE1] interface Bridge 1
[PE1-Bridge1] pw 100 binding vc 100 destination 10.1.2.1 pw-template VPWS-TPL1

# ========== PE2 配置 ==========
[PE2] interface Bridge 1
[PE2-Bridge1] port gigabitethernet 1/0/0 1

[PE2] pw-template VPWS-TPL1
[PE2-pw-template-VPWS-TPL1] pw-type vlan
[PE2-pw-template-VPWS-TPL1] control-word
[PE2-pw-template-VPWS-TPL1] ipv4 10.1.1.1 32
[PE2-pw-template-VPWS-TPL1] vc-id 100

[PE2] interface Bridge 1
[PE2-Bridge1] pw 100 binding vc 100 destination 10.1.1.1 pw-template VPWS-TPL1
4.2 验证 PW 状态
# 查看PW状态
<PE1> display pw brief
  Total PW number: 1
  PW-Index  Destination   VC-ID  State   Protocol  PW-Type
  100       10.1.2.1      100    Up      LDP       Vlan

# 查看PW详细信息
<PE1> display pw interface Bridge 1 pw-index 100
  PW Index: 100
    Destination: 10.1.2.1
    VC-ID: 100
    State: Up
    PW Type: Vlan
    Control Word: Enabled
    Local Label: 16001
    Remote Label: 16002
    Ingress: Bridge1
    Statistics:
      Input:  Packets=15234, Bytes=1523400
      Output: Packets=15100, Bytes=1510000
4.3 故障排查:PW 状态 Down
故障场景:PW 状态为 Down,CE 间二层通信中断。
# Step 1: 检查 PW 状态
<PE1> display pw interface Bridge 1 pw-index 100
  State: Down
  # 查看Down原因

# Step 2: 检查对端可达性
<PE1> ping -a 10.1.1.1 10.1.2.1
  # 可达

# Step 3: 检查 LDP 标签
<PE1> display mpls lsp 10.1.2.1 32
  # LDP标签正常

# Step 4: 检查 PW 信令
<PE1> debugging mpls l2vc
<PE1> terminal debugging
  # 发现: 收到Label Withdraw, 对端PW被删除

# Step 5: 在对端检查
<PE2> display pw interface Bridge 1 pw-index 100
  State: Down
  Error: VC-ID mismatch
  # 根因: PE2的VC-ID配置为200, PE1配置为100, 不匹配!

# Step 6: 修正
[PE2-pw-template-VPWS-TPL1] vc-id 100
五、总结
| 项目 | 要点 |
|---|---|
| VPWS | 点到点二层链路仿真,通过 PW 标签标识 |
| PWE3 | IETF 标准,定义 PW 信令、封装和控制机制 |
| 双层标签 | 公网 LDP 标签(外层)+ PW 标签(内层) |
| Control Word | 提供序列号和长度标识,推荐启用 |
| VC-ID | PW 唯一标识,两端必须匹配 |
思考
- VPWS 是点到点连接。如果需要实现多点二层互通(如一个以太网段),应该使用什么技术?
- PW 的 Control Word 是可选字段。如果不启用 Control Word,会对 PW 传输造成什么影响?
- VPWS 使用 LDP 信令建立 PW。如果网络使用 SR-MPLS 而非 LDP,PW 还能正常工作吗?
下篇预告:第170篇:VLL(Virtual Leased Line)点到点二层 VPN